

A series of high-profile disruptions affecting major parts of American life unfolded over the past week, including a nationwide ground stop that disrupted air travel, banking outages at JPMorgan Chase and other lenders, and a service interruption at Microsoft. Despite the breadth of the incidents, officials quickly assured the public that there was no evidence of malicious activity.
During the ground stop, Homeland Security Secretary Markwayne Mullin said the nation’s homeland and banking systems remained secure. He maintained that the disruptions did not appear to be connected to a cyberattack or other deliberate action.
Director of National Intelligence Jay Clayton offered a similar assessment, saying officials had found no evidence of a coordinated or state-sponsored attack. Instead, he pointed to routine patching, maintenance and system upgrades.

Director of National Intelligence Jay Clayton testified Wednesday that intelligence indicated the recent outages were unrelated and not the result of a “state-sponsored” attack. (Brendan Smialowski / AFP)
“Based on what we know today … these are separate service outages associated with maintenance and technical changes,” Clayton told the House Homeland Security Committee on Wednesday. “They are not a coordinated or state-sponsored attack.”
Microsoft, JPMorgan Chase and other major companies likewise attributed the interruptions to internal technical problems or software bugs, rather than hostile intrusions.
Danny Cooper, CEO of critical infrastructure security firm SMET, said the speed of those assurances raises questions.
“A blanket statement like ‘there’s no malicious activity associated with any of the outages’ is almost impossible from a probability perspective,” Cooper told News Media.

A Chase ATM is shown outside the bank as technology problems disrupt banking services. (Ava Palschakov for News Media)
After a major disruption, public concern often centers on one question: Was it an accident or an attack? Cooper said skepticism is understandable given that numerous critical systems experienced problems within a five- or six-day period.
“How plausible is it that all these pillars or whatever all suffered major independent technical failures within a five- or six-day window?” Cooper asked. “I think highly improbable. And I understand why the American public is calling this into question and deeply empathize with that. The pattern recognition is there.”
Even when officials cite routine maintenance or aging equipment, Cooper said, dismissing the possibility of foul play too early can bypass investigative steps that require time. That could make it harder to identify weaknesses, address them and prevent similar incidents in the future.

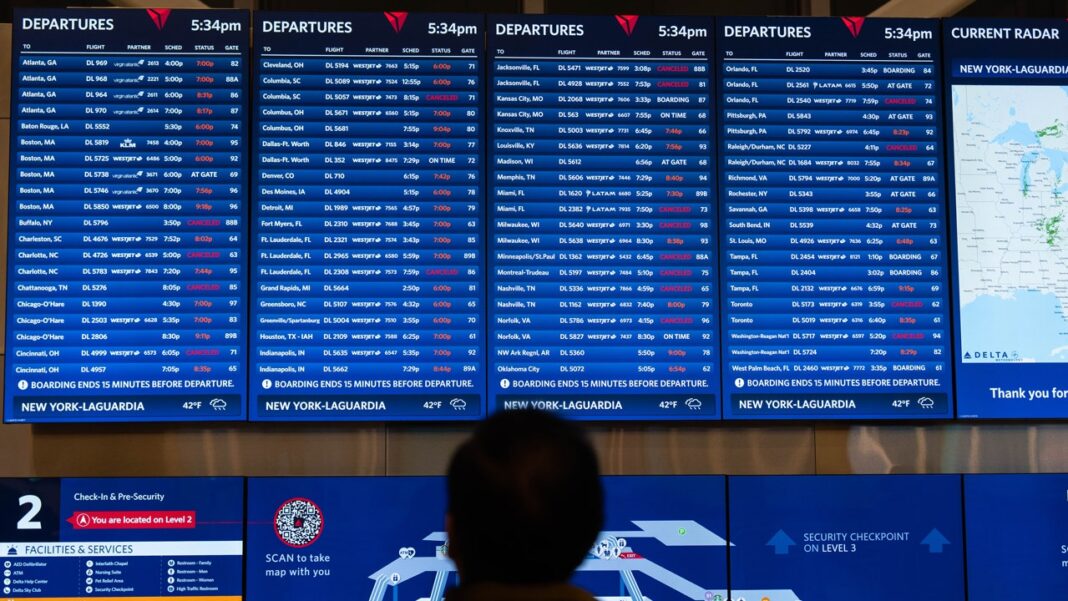
A person views a departures board displaying delays and cancellations at LaGuardia Airport on Nov. 13 in New York City. The Federal Aviation Administration ordered a nationwide ground stop for all departing flights, marking one of several critical infrastructure disruptions reported last week and prompting questions about their causes. (Getty Images)
“If a company or the government is making a statement that is as bold as ‘we are certain there is no malicious activity here’ without having the time to actually do an appropriate investigation, in the case of this sort of cyber domain, some cyber forensics and a full audit of what transpired, that’s not quite how it works,” Cooper said.
“On the physical side, being able to fully interrogate what has happened in the environment, who was there, and so on about what is happening in the periphery and what led up to that moment in time, those things take time.”
Cooper said an immediate “nothing to see here” response can intensify public suspicion, especially when several agencies and institutions repeat the same conclusion before audits are complete.
The Democratic National Committee also criticized what it described as conflicting explanations from the Trump administration.

A general view of Charlotte Douglas International Airport in Charlotte, North Carolina, on Nov. 13, 2026, as passengers faced delays and cancellations after the Federal Aviation Administration issued a nationwide ground stop for all flights. (Peter Zay/Anadolu via Getty Images)
“The administration has repeatedly offered conflicting statements about the causes of the outages,” DNC Deputy Communications Director Kendall Witmer said in a statement. “Homeland Security Secretary Markwayne Mullin suggested that SI – Trump’s preferred name for Artificial Intelligence (AI) – is responsible for the multiple outages that have occurred in recent days, according to a ‘very smart’ tech guy he talked to. Then, yesterday, Secretary of State Marco Rubio contradicted Mullin and would not attribute the outages to AI.”
Much of the official explanation for the November disruptions focused on software updates and system upgrades. Cooper noted that organizations routinely schedule maintenance, but downtime can occur when large-scale changes are deployed, particularly if teams move too quickly.
At the same time, those maintenance windows can create opportunities for sophisticated adversaries, Cooper warned.
“If companies are disproportionately moving to execute these sorts of upgrades en masse, then yes, it’s possible that you would have a higher number of downtime or outages,” Cooper said.
“But it’s also quite possible that, particularly given the sophistication of cyber adversaries, whether it’s hackers, whether it’s non-state entities, whether it’s nation-state entities, it’s also possible that they are using those software updates or upgrades or patches and in those moments actually injecting malware and exploits and so on.”