

Thousands of people were abruptly cut off from the digital world last week when a widespread Microsoft account outage dragged on for roughly 24 hours.
That disruption, however, appeared to be only the opening act in a week of cyber turmoil that has fueled fears of a coordinated attack, amid reports of a possible radioactive “dirty bomb” plot on US soil.
Chris Swecker, a former senior FBI official, told the Daily Mail that the United States is facing its “highest threat level since 9/11.”
In the aftermath of the Microsoft failure, the Federal Aviation Administration (FAA) imposed an hours-long ground stop on all flights—the longest such halt since the September 11 terror attacks. Customers at several major US banks also reported service interruptions, while a separate system outage at United Airlines delayed flights.
By Tuesday, reports emerged that malicious JavaScript had been delivered to visitors at 178 major organizations through the Optimizely platform. The National Security Agency’s highly classified internal communications network then went offline, followed by Apple, where users were temporarily locked out of their accounts.
The disruptions came as new US intelligence reportedly warned that Iran was considering attacks against senior Trump administration officials in Washington, potentially involving a radioactive “dirty bomb” or chemical weapon. The security concerns have already prompted Treasury Secretary Scott Bessent to join other cabinet officials in moving into military housing.
Cybersecurity experts told the Daily Mail how such an attack might unfold and which targets could be vulnerable, raising alarms even as officials described the recent technology failures as unrelated technical problems.
“There’s too much smoke to rule out that there’s fire here,” John Miri, who runs the Electric Grid Cybersecurity Alliance, a group of executives working to protect power grids and other utilities from hackers, told the Daily Mail.

The string of cyber incidents has intensified anxiety among Americans

The FAA’s hours-long ground stop on Friday brought airport operations to a standstill
Threat of cyberattacks
Microsoft said it found no evidence of malicious activity behind last Thursday’s outage. Instead, the company attributed the problem to a flaw introduced in July while changes were being made to its cloud gateway.
Transportation Secretary Sean Duffy blamed the airline disruption on contractor L3Harris, which was replacing an aging copper connection with fiber at a remote facility in El Dorado, Arkansas, when the network became overwhelmed.
Homeland Security Secretary Markwayne Mullin likewise said the country was not under cyberattack, arguing that newer technology had overloaded older systems.
President Donald Trump struck a similarly relaxed tone. Asked about the outages during a visit to the Philippines, he told reporters that “things like that happen” and said, “It’s fine.”
Miri remains unconvinced, arguing that the “pattern’s starting to become undeniable.”
“It’s very easy to hide behind this statement of ‘we have no evidence of a cyber attack,’” he said. “We have no evidence that there’s any gold missing from the vault… The problem with cyber attacks is that the evidence is not always found right away.”
If cyberattacks were involved, Miri said, they appeared targeted and precise—not like the digital equivalent of flattening an entire city block.
His assessment, which depends on the incidents being connected to an attack, is that the past week unfolded in two distinct waves.
The first wave, affecting Microsoft, the FAA and banks, resembled the work of a sophisticated nation-state, he said. The targets were major organizations, the consequences were significant and the sequence appeared orderly—similar to the SolarWinds espionage campaign attributed to Russia and discovered in 2020.

Miri said any attacks appeared targeted and precise rather than designed to cause indiscriminate digital destruction

John Miri leads the Electric Grid Cybersecurity Alliance, which works to protect power grids and other utilities from hackers
The second wave, by contrast, looked more opportunistic and financially motivated. Smaller organizations were hit by smaller attacks, Miri said, a pattern consistent with copycats using newly available AI tools to exploit a country that appeared vulnerable. Utilities often see similar surges in attacks after floods, hurricanes and winter storms, when incidents “go through the roof.”
James Knight, a principal at cybersecurity company Digital Warfare, said the Optimizely incident showed the characteristics of a criminal operation rather than a state-sponsored campaign.
“This is the MO of a hacking group,” he said, describing the attackers as “opportunistic cybercriminals focused on financial theft.”
The incidents showed “different failure modes with different technical signatures,” Knight said. He rated his confidence that they were connected as “low.”
If a nation-state was responsible for the first wave, Knight said, the likely candidates would be Iran, Russia or China. North Korea, he argued, is more focused on ransomware, which helps generate revenue despite international sanctions.
Miri said national security officials have warned for at least a decade that China could use cyber disruption to distract Washington. He also suggested a less direct motive: damaging confidence in American technology and undermining the country’s lead in the global artificial intelligence race.
The timing has drawn attention. Trump, Chinese President Xi Jinping and Russian President Vladimir Putin are scheduled to meet Thursday in Shenzhen, the host city for this week’s Asia-Pacific Economic Cooperation summit.
Even so, Miri does not believe the country is being prepared for a devastating final strike.
“If your goal was really to shut America down, you’d do it all at once,” he said.
The banks experienced disruptions but were not taken offline, he noted. No one has permanently lost money, and Microsoft’s data was not erased.
“I think this may be about humiliating us,” Miri said. “It may be about taking us down a few pegs. It may be about slowing us down.”

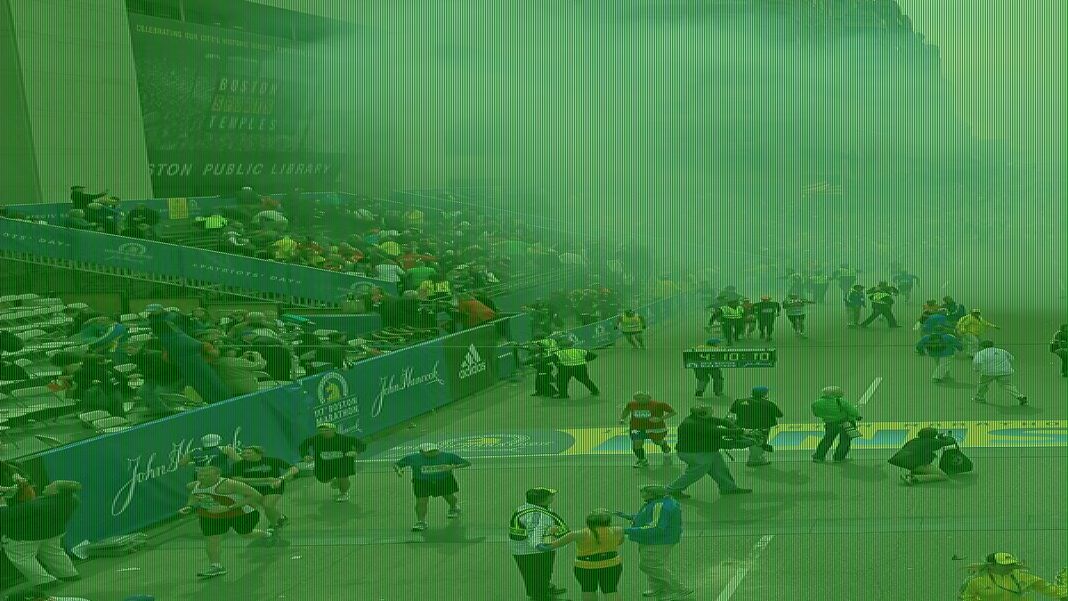
Reports this week said Iran was developing plans to target senior Trump administration officials in the nation’s capital with a radioactive “dirty bomb” or chemical weapon. Swecker said the physical blast could resemble the device used at the 2013 Boston Marathon
Dirty bomb threats
The cyber disruptions emerged as reports claimed Iran was considering a “dirty bomb” attack in Washington, DC. Such a device disperses radioactive material through an explosion, potentially contaminating streets, homes and businesses.
Sources familiar with the intelligence told CNN that the reported plans included specific locations and targets, while stressing that the information did not point to an imminent attack.
White House officials have held several meetings to discuss how to counter the threat, according to sources cited by CNN. However, spokesperson Lauren Bis said there were “no credible threats to the homeland.”
Swecker, a 24-year FBI veteran, told the Daily Mail that a dirty bomb could be assembled by rogue individuals already inside the United States or smuggled across the southern border in recent years.
“Because we have a fierce conflict with Iran right now, who are tenacious in trying to do this country in, we’ve got conflict in Ukraine, all our enemies are on the move. This is a time when enemies are circling the waters,” he said.
A potential Iranian dirty bomb attack, Swecker added, would probably strike a “target of opportunity” rather than a prominent landmark such as the White House or the Capitol.
The initial blast would be comparable to that of a conventional explosive device, such as the bomb used at the Boston Marathon in 2013.
The greatest danger, Swecker said, would come from radiation exposure—not structural damage—particularly if the device detonated in a densely populated area such as New York’s Times Square.
“The fallout’s gonna affect people, and that depends on the wind, the density of the population there [and] how quickly that area can be evacuated,” he explained.
Drawing on his experience in Iraq, Swecker said terrorists typically strike whatever appears most vulnerable at a given moment. Their wider objective, he argued, would not be to destroy the United States but to spread fear and intensify divisions within American society.
“They’re just trying to sow terror in the United States. They can’t bring this country down in any way, even with a dirty bomb. They’ll never defeat this country with terrorism, but they want to turn us against each other,” Swecker said.

Chris Swecker spent 24 years with the FBI

Swecker said drones were his leading concern when it came to potential terrorist attacks
Drone attack fears
Swecker identified drones as his greatest concern when assessing potential terrorist attacks.
After cyberattacks targeting critical US infrastructure—including the power grid and financial centers—he described drones as one of the country’s most serious emerging threats.
With so many legitimate drones already operating in American skies, distinguishing a hostile aircraft would be exceptionally difficult, he said, and there is no obvious solution to the challenge.
“I don’t want to plant any ideas,” he said, “but I think we can all imagine what a drone could do in a densely populated area.”